1
1
ISO/IEC 27001 Certified
Secure. Auditable. Proven.
Internationally recognized information security with controlled access, encrypted data transfer and traceable digital processes — already reviewed for use in German public health and justice environments.
1
Data Protection
Security in Accordance with 27001 Requirements
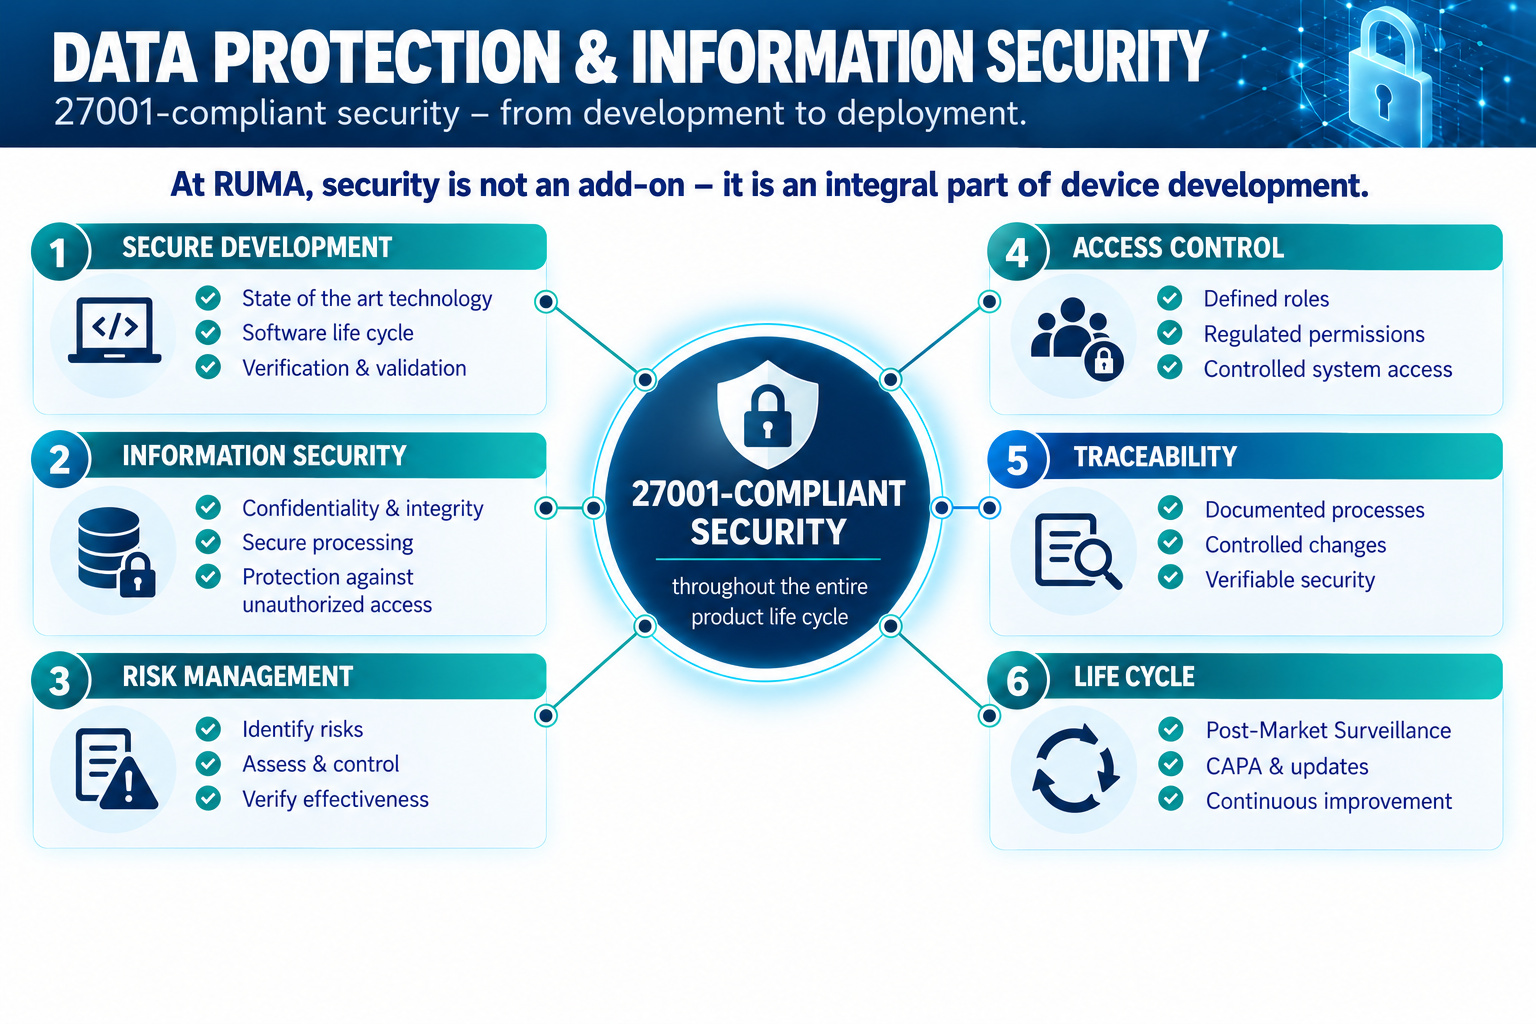
Security is not an additional feature. It is an integral part of device development.
Data Protection & Information Security
RUMA incorporates data protection and information security into the development, operation and monitoring of its digital device from the outset.
ISO/IEC 27001 requires software to address risk management, information security, verification and validation throughout the software lifecycle.
1. Secure Software Development
Security from the outset
- Development in accordance with the state of the art
- Defined software lifecycle
- Documented security requirements
- Software verification and validation
Benefit: Security is not added retrospectively but is an integral part of product development.
2. INFORMATION SECURITY
Protecting sensitive information as a product requirement
- Protection of confidentiality
- Protection of information integrity
- Secure processing
- Protection against unauthorised access
Benefit: Sensitive information is processed within a regulatory framework with defined security requirements.
3. Access Protection
Access for authorised users only
- Defined user roles
- Regulated permissions
- Controlled system access
- Protection against unauthorised access
Benefit: Access to system functions and information is restricted and can be controlled.
4. RISK MANAGEMENT
Identify, assess and control risks
- Systematically identify risks
- Assess risks
- Define appropriate protective measures
- Verify the effectiveness of these measures
- Continuously incorporate new findings
Benefit: Security risks are addressed throughout the entire product lifecycle rather than at isolated points.
5. Verification & Validation
Security must be demonstrable
- Requirements are documented
- Functions are tested
- Security measures are reviewed
- Software is verified and validated before deployment
- Changes are subject to controlled processes
Benefit: Both system functionality and secure operation are systematically verified.
6. Security Throughout the Product Lifecycle
Develop → Test → Monitor → Improve
- Responsibility does not end when the product is placed on the market.
- Ongoing monitoring
- Assessment of emerging risks
- Controlled updates
- Corrective and improvement measures
- Post-market surveillance
- Continuous development
Benefit: The security of the medical device continues to be assessed throughout its operational life.
THE ADVANTAGES
For patients
Protection of sensitive information · controlled access · secure digital processes
For organisations
Traceable security structures · clearly defined responsibilities · verifiable processes
For RUMA
Security as an integral part of the device – from development to deployment.